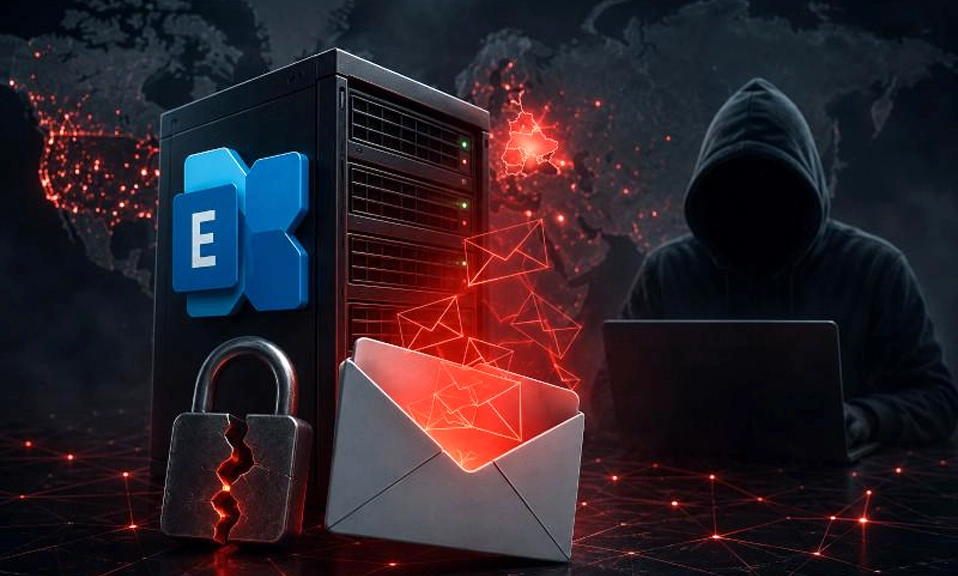
Your organization’s email server, the unassuming digital post office that handles everything from internal memos to client contracts, has quietly become one of the most prized targets for sophisticated cybercriminals. The threat has evolved beyond simple spam and generic phishing. A new wave of malware and attack techniques is turning the email server itself from a delivery mechanism into a weapon, a hiding place, and a permanent espionage post.
The danger is not theoretical. In late 2025, security researchers from ESET uncovered a previously undocumented malware toolkit named Cereal, specifically designed to operate deep within Microsoft Exchange servers. This toolkit, attributed to the Russia-aligned Turla APT group, represents a significant leap in tradecraft. It is not designed to simply steal credentials and leave; its purpose is long-term, stealthy cyber espionage.
The New Threat: When the Server Becomes the Spy
What makes Cereal so alarming is its operational philosophy. Traditional malware often “calls home” to an external command-and-control (C2) server to receive instructions, a communication pattern that security tools can detect and block. Cereal fundamentally subverts this.
No External C2: The malware turns the victim’s own Exchange server into its command center. It abuses legitimate web paths like Outlook Web Access (OWA), Autodiscover, and ActiveSync to receive instructions, making malicious traffic nearly indistinguishable from normal employee activity.
Living in Memory: The components of the toolkit are modular .NET code that is encrypted and decrypted directly in memory, leaving almost no trace on the server’s disk.
Intercepting the Mail Stream: The most insidious component, CerealBox, is injected directly into
EdgeTransport.exe, the very process responsible for handling email transport. This allows the attackers to examine every email that passes through the server, identify messages of interest—filtering for documents like.docor.docxfiles—and quietly set aside a copy for exfiltration, all while the original email is delivered without a hitch.
This tradecraft is not likely to remain the exclusive domain of nation-state actors. As one industry expert noted, “Criminal groups study nation-state techniques the way minor leaguers study a big league pitcher’s grip. What works in the majors eventually shows up in every ballpark”.
The Scale of the Problem: From Espionage to a Global Relay Network
While Cereal demonstrates the depth of a targeted espionage campaign, other threat actors are using compromised email infrastructure at a massive scale for profit. In 2026, researchers uncovered PCPJack, a threat actor who had compromised 230 cloud servers across Amazon Web Services, Google Cloud, and Microsoft Azure.
These servers were not used to send malware or steal data directly. Instead, they were converted into a covert SMTP relay network. Each compromised server was assigned a dedicated proxy port, creating a resilient and hard-to-trace infrastructure for distributing spam, phishing emails, and smishing (SMS phishing) campaigns worldwide. This kind of network allows attackers to bypass reputation-based email filters, as the emails are sent from reputable cloud IP addresses.
This trend is part of a broader shift where nation-state actors are systematically targeting email infrastructure. Recent campaigns have exploited vulnerabilities in platforms like Zimbra and Roundcube to gain a foothold, treating the email server not as an end goal, but as a gateway into an entire enterprise environment.
Why Email Servers Are the Perfect Target
The attractiveness of email servers to attackers is rooted in a simple reality: they are both essential and exposed.
They sit on the public internet: To function, email servers must be accessible to the outside world, making them a constant target for automated scanning and probing.
They are the keys to the kingdom: A compromised email server often provides a direct path to reset passwords for other critical services, access sensitive internal communications, and launch further attacks from a trusted source.
The human element is the weakest link: The vast majority of attacks still rely on tricking a human. In the first quarter of 2026 alone, Microsoft observed 8.3 billion phishing emails, and Business Email Compromise (BEC) attacks—where attackers impersonate a trusted figure to request money or data—totalled 10.7 million. The average cost of a single BEC incident is a staggering $123,005.
Fortifying Your Digital Post Office
Defending against these advanced threats requires a layered approach that goes beyond a single security product. The fundamentals of email security remain critical, but they must be rigorously enforced.
Patch Relentlessly: The initial access vector for many of these attacks is an unpatched vulnerability. The Cereal campaign and the Zimbra attacks all relied on flaws for which patches existed. Ensure that your email server software and all related systems are up to date.
Implement Strong Authentication: Deploy SPF, DKIM, and DMARC with an enforcement policy of
reject. This prevents attackers from spoofing your domain and makes it much harder for them to impersonate your brand or employees.Enforce Phishing-Resistant MFA: Multi-factor authentication is non-negotiable, but not all MFA is equal. Switch to phishing-resistant methods like FIDO2 security keys or passkeys, especially for administrator and high-value accounts. Attackers have become adept at bypassing SMS- or app-based MFA using adversary-in-the-middle (AiTM) phishing kits.
Adopt AI-Powered Defense: Traditional email gateways that only look for malicious links or attachments are no longer sufficient. Modern AI-driven email security solutions analyze communication patterns, behavioral anomalies, and intent to detect advanced phishing and BEC attacks that rely on social engineering rather than obvious technical payloads.
Monitor and Hunt for Threats: Assume that prevention may fail and build capabilities to detect and respond. Since malware like Cereal leaves few artifacts on disk, organizations need to monitor for suspicious activity in memory, unusual network connections from email server processes, and anomalous access logs for endpoints like OWA and ActiveSync.
The email server is no
longer just a conduit for communication; it is a high-value target in the crosshairs of both sophisticated espionage groups and profit-driven cybercriminals. The threat has moved from trying to break in through the front door to living silently in the walls, reading the mail as it passes. For businesses, the message is clear: a passive, set-and-forget approach to email security is a liability. The digital post office needs a modern, layered defense—one that combines rigorous patching, strong authentication, and the kind of intelligent, behavior-based detection that can spot the quiet, persistent intruder before the damage is done.